*作者:让科技赋能制造
本文要点
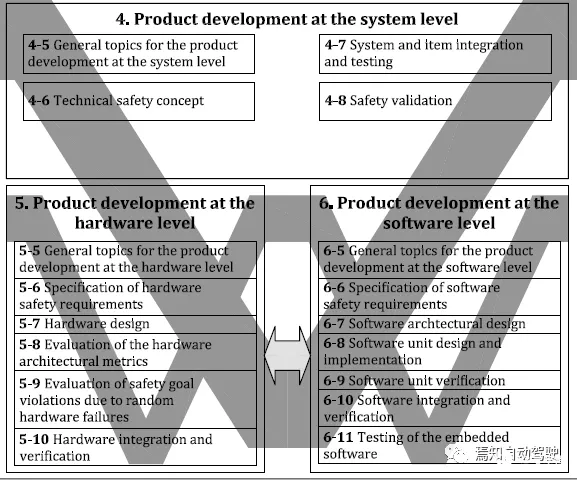
ISO 26262 将功能安全开发融入了广为熟知的「V 模型」开发流程中。根据系统 / 软件 / 硬件三个层级的划分,ISO 26262 的功能安全开发活动被融入了三个「V 模型」之中,如下图所示。在前面的系列文章中已经对这三个「V 模型」中包含的功能安全开发要点进行了说明。
做工程项目的朋友都知道,对于一款量产产品,除了完成开发工作以外,还需要对开发产物进行审核,审核通过后方能释放产品。功能安全开发也是如此。「ISO 26262,part 2,功能安全管理」中详细介绍了功能安全的审核流程和要求,对应的术语为「认可措施,Confirmation measures」。
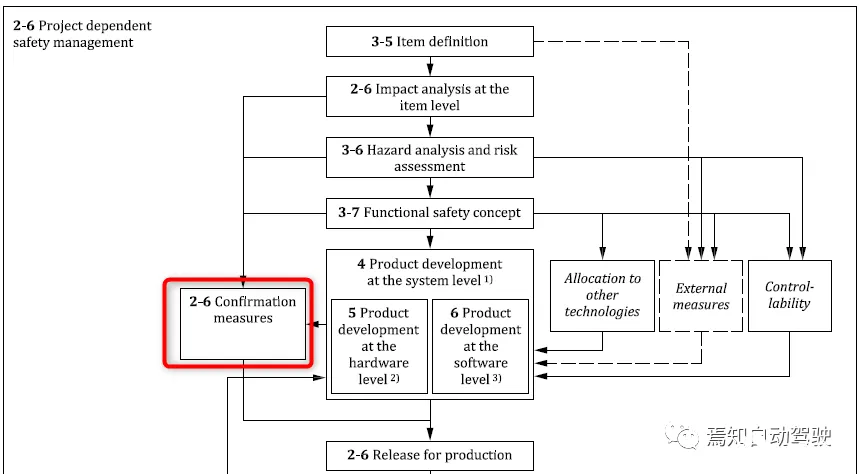
一个现实的情况是,当读者实际上去读 ISO 26262 中「认可措施,Confirmation measures」相关的解释和要求时,很容易就被其中包含的三个维度的措施给绕晕了,尤其是结合中文国标 GB / T 34590 对这三个维度的翻译更加混淆,如下所示:
-
Confirmation review (认可评审)
-
Functional safety audit (功能安全审核)
-
Functional safety assessment (功能安全评估)
基于此,本文将试图对「认可措施,Confirmation measures」以及其中包含的三个维度的措施进行辨析,旨在为读者提供有价值的参考。
Note:
-
考虑到中文翻译的混淆性,除非有必要,本文接下来将使用英文概念进行描述。
-
ISO 26262-2018 版对 confirmation measures 的解释和要求相比 2011 版做了很多补充,建议读者阅读 2018 版方便理解。
- Confirmation measures 及其三个维度
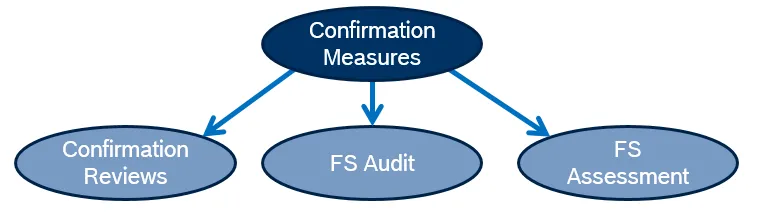
如前所述,Confirmation measures 的主要目的是对功能安全开发过程及产物进行评估,以确认是否满足 ISO 26262 的要求。而这一评估需要从三个维度来展开,如下图所示。
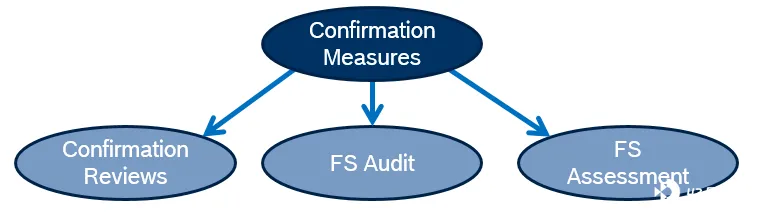
这三个维度的对象及目的如下:
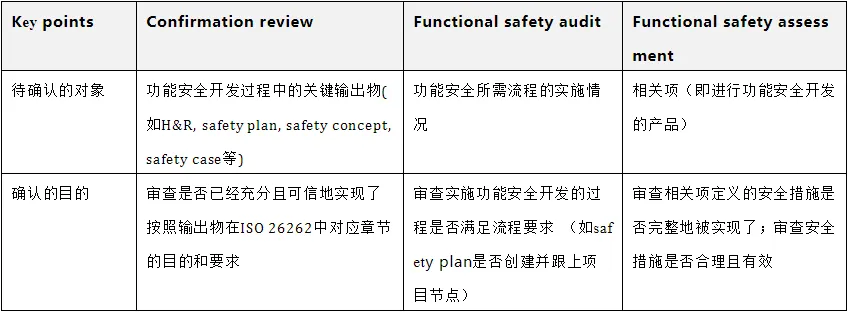
从上面的对比可以简单总结出,confirmation review 和 functional safety audit 不关注相关项设计的安全措施是否合理,而只关注安全措施在实施的过程中有没有按照 ISO 26262 要求开发;而 functional safety assessment 的重点在于评估在安全措施符合开发要求的情况下,是否真的能够实现功能安全。
基于上面的角度,可以看出实际上三个维度并不是孤立的。
一方面既然安全措施按照 ISO 26262 要求实施是进行 functional safety assessment 的前提,那么从项目开发灵活性的角度,根据项目复杂程度的不同可以合理变通。对于比较简单的项目,实际上在进行 functional safety assessment 审核的时候可以一并进行 confirmation review 和 functional safety audit,而不需要强行分成三个活动。ISO 26262 中对这一点有所提及:
ISO 26262-2018, part2, 6.4.9.1
NOTE 7 Confirmation measures such as confirmation reviews and functional safety audits can be merged and combined with the functional safety assessment to support the handling of comparable variants of an item.
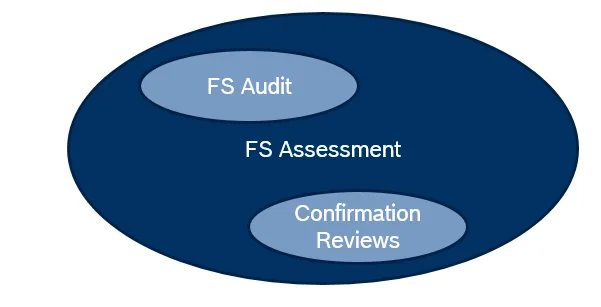
另一方面,confirmation review 和 functional safety audit 的结果可以作为 functional safety assessment 的输入,这样在进行 assessment 时就可以默认安全措施已经被实现,只需要重点关注其合理性和有效性。这一点在 ISO 26262 中也有提及。
ISO 26262-2018, part2, 6.4.12.8
A functional safety assessment shall consider:
a ) …
b ) the results from the confirmation reviews and functional safety audit;
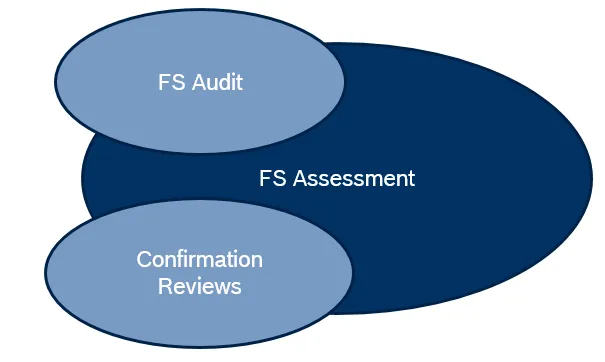
上述对比的目的是辨析 Confirmation measures 的三个维度的区别,接下来将对这三个维度进行进一步说明。 于此同时,既然是「审查」,那么就需要确定「审查员」。在工程开发中,对「审查员」是有独立性要求的,接下来也会对这一部分进行说明。
- Confirmation review (认可评审)
前面提到, Confirmation review 的评审对象是功能安全开发过程中的关键输出物(如 H & R, safety plan, safety concept, safety case 等),所以按照 safety plan 的计划,当相应的输出物完成后即可以发起 Confirmation review。在产品 SOP 之前所有的输出物的 confirmation review 工作都需要完成。
ISO 26262-2018, part 2 中补充了审核员 reviewer 的要求:
6.4.10.3: To increase confidence in the achievement of the review objectives, the reviewer checks the correctness, completeness, consistency, adequacy and contents of the work product against the corresponding requirements of the ISO 26262 series of standards.
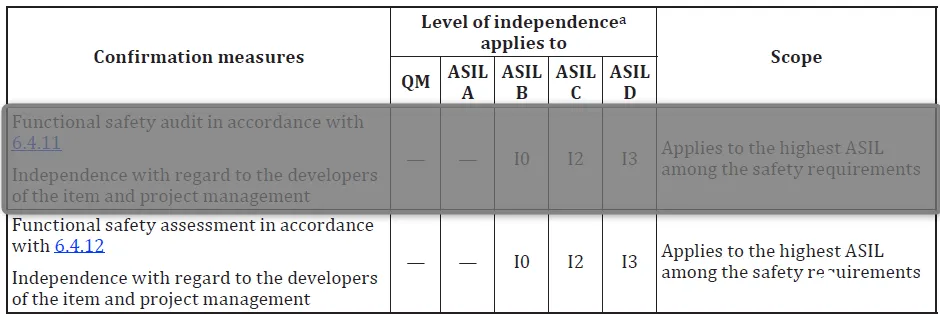
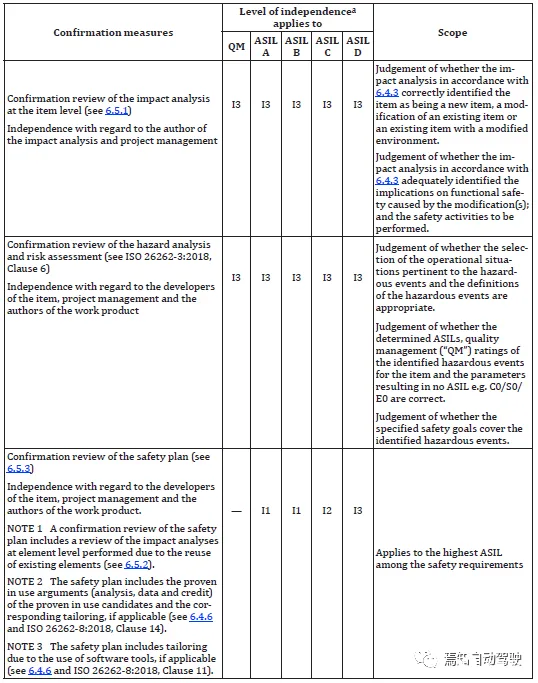
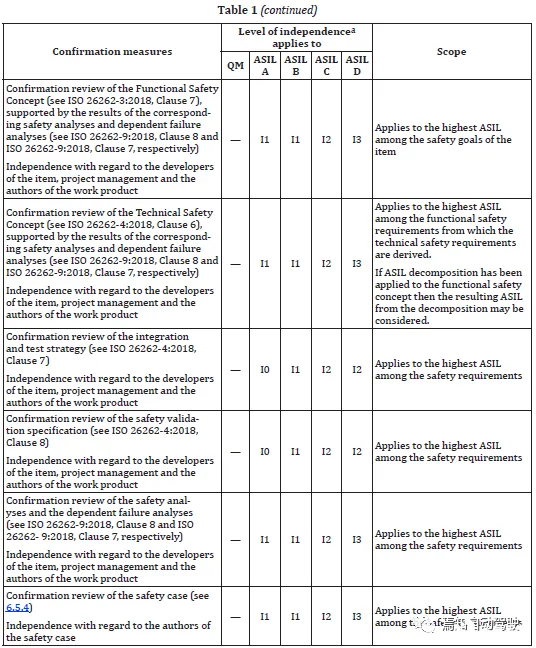
而 reviewer 的独立性要求根据功能安全要求的 ASIL 等级的不同而不同,ASIL 等级越高,独立性要求更加严苛。ISO 26262 的独立性要求如下图所示。
图中标注部分的释义如下:
-
I 0: 宜执行认可措施; 但如果执行, 应由不同的人员执行;
-
I 1: 认可措施应由不同的人员执行;
-
I 2: 认可措施应由来自不同团队的人员执行, 即不向同一个直接上级报告;
-
I 3: 认可措施应由来自不同的部门或组织的人员执行, 即在管理、资源和发布权限方面与负责相关工作成果的部门是独立的。
- Functional safety audit (功能安全审核)
ISO 26262-2018, part 2 中补充了 Functional safety audit 的目的:
6.4.11.3: A functional safety audit may be based on a judgement of whether the process related objectives of the ISO 26262 series of standards are achieved. (功能安全审核可以基于 ISO 26262 标准中定义的和流程相关的目标所对应的流程来判断。)
ISO 26262-2018 版中将定义的和流程相关的目标概括为 a) ~ g),因此 audit 也基于这些点来展开。
a ) an evaluation of the implementation of the processes against the definitions of the activities referenced or specified in the safety plan;
b ) an evaluation of the safety plan products against the organization-specific rules and processes;
c ) an evaluation of the arguments, if provided, as to why the process related objectives of the ISO 26262 series of standards are achieved;
d ) an evaluation of whether the work products required by the safety plan are available;
e ) to define the tailored safety activities, to provide the corresponding rationales for tailoring and to review the provided rationales;
f ) an evaluation of whether the work products required by the safety plan comply with ISO 26262-8:2018, 10.4.3 and are consistent between one another;
g ) improvement recommendations in accordance with 5.4.2.6, if applicable, e.g. in the case of noncompliances.
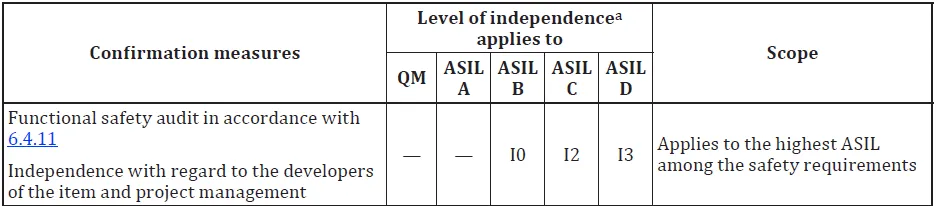
对于审核员 auditor 的独立性要求根据功能安全需求的 ASIL 等级的不同而不同,ASIL 等级越高,独立性要求更加严苛。
- Functional safety assessment (功能安全评估)
ISO 26262 中要求 functional safety assessment 的评估范围应至少包括如下三个方面:
-
安全计划要求的工作成果;
-
功能安全要求的流程;
-
对在相关项开发过程中已实施的且可评估的安全措施进行适宜性和有效性评审。
从这里我们可以看出,functional safety assessment 相比其他两个而言可以被认为是更为全面的评估,同时也验证了前文提到的的 confirmation review 和 functional safety audit 可以作为 assessment 的输入。
那么既然 functional safety assessment 的全面性更强,什么时候开展 assessment 呢?总的来说,对于复杂的项目而言,assessment 应该尽早计划而不是压到最后的项目释放节点之前。ISO 26262-2018 补充的建议如下:
6.4.12.3 A functional safety assessment:
a ) shall be planned in accordance with 6.4.6.5 f);
b ) should be planned at the latest at the beginning of the product development at the system level;
c ) should be progressively performed during the product development; and
d ) shall be finalized before the release for production.
对于评估员 assessor 的独立性要求根据功能安全需求的 ASIL 等级的不同而不同,ASIL 等级越高,独立性要求更加严苛。